BUSINESS VOIP & UNIFIED COMMUNICATIONS
See threats sooner. Respond faster.
Gain 24x7x365 visibility across your IT environment with HDUK SOC & SIEM, combining intelligent threat detection with experienced security analysts to identify, investigate and respond to suspicious activity.
See threats sooner. Respond faster.
Gain 24x7x365 visibility across your IT environment with HDUK SOC & SIEM, combining intelligent threat detection with experienced security analysts to identify, investigate and respond to suspicious activity.
Cyber threats don't wait to be noticed
Cyber threats continue to evolve in both volume and sophistication. Traditional security tools alone are no longer enough to identify modern attacks, particularly when security activity is spread across users, devices, cloud platforms and network systems.
SOC & SIEM provides continuous visibility across your IT environment, helping identify abnormal behaviour and suspicious activity before it develops into a security incident.
SOC & SIEM provides continuous visibility across your IT environment, helping identify abnormal behaviour and suspicious activity before it develops into a security incident.
CONTINUOUS SECURITY OPERATIONS
Your IT environment, monitored around the clock
HDUK SOC & SIEM continuously monitors security activity across your IT estate, bringing together intelligent analysis and experienced security analysts to identify and investigate potential threats.
Monitor
Maintain 24x7x365 visibility across users, endpoints, servers, cloud platforms, Microsoft 365 services and network infrastructure.
Investigate
Experienced security analysts review significant alerts, validate potential threats and determine what requires action.
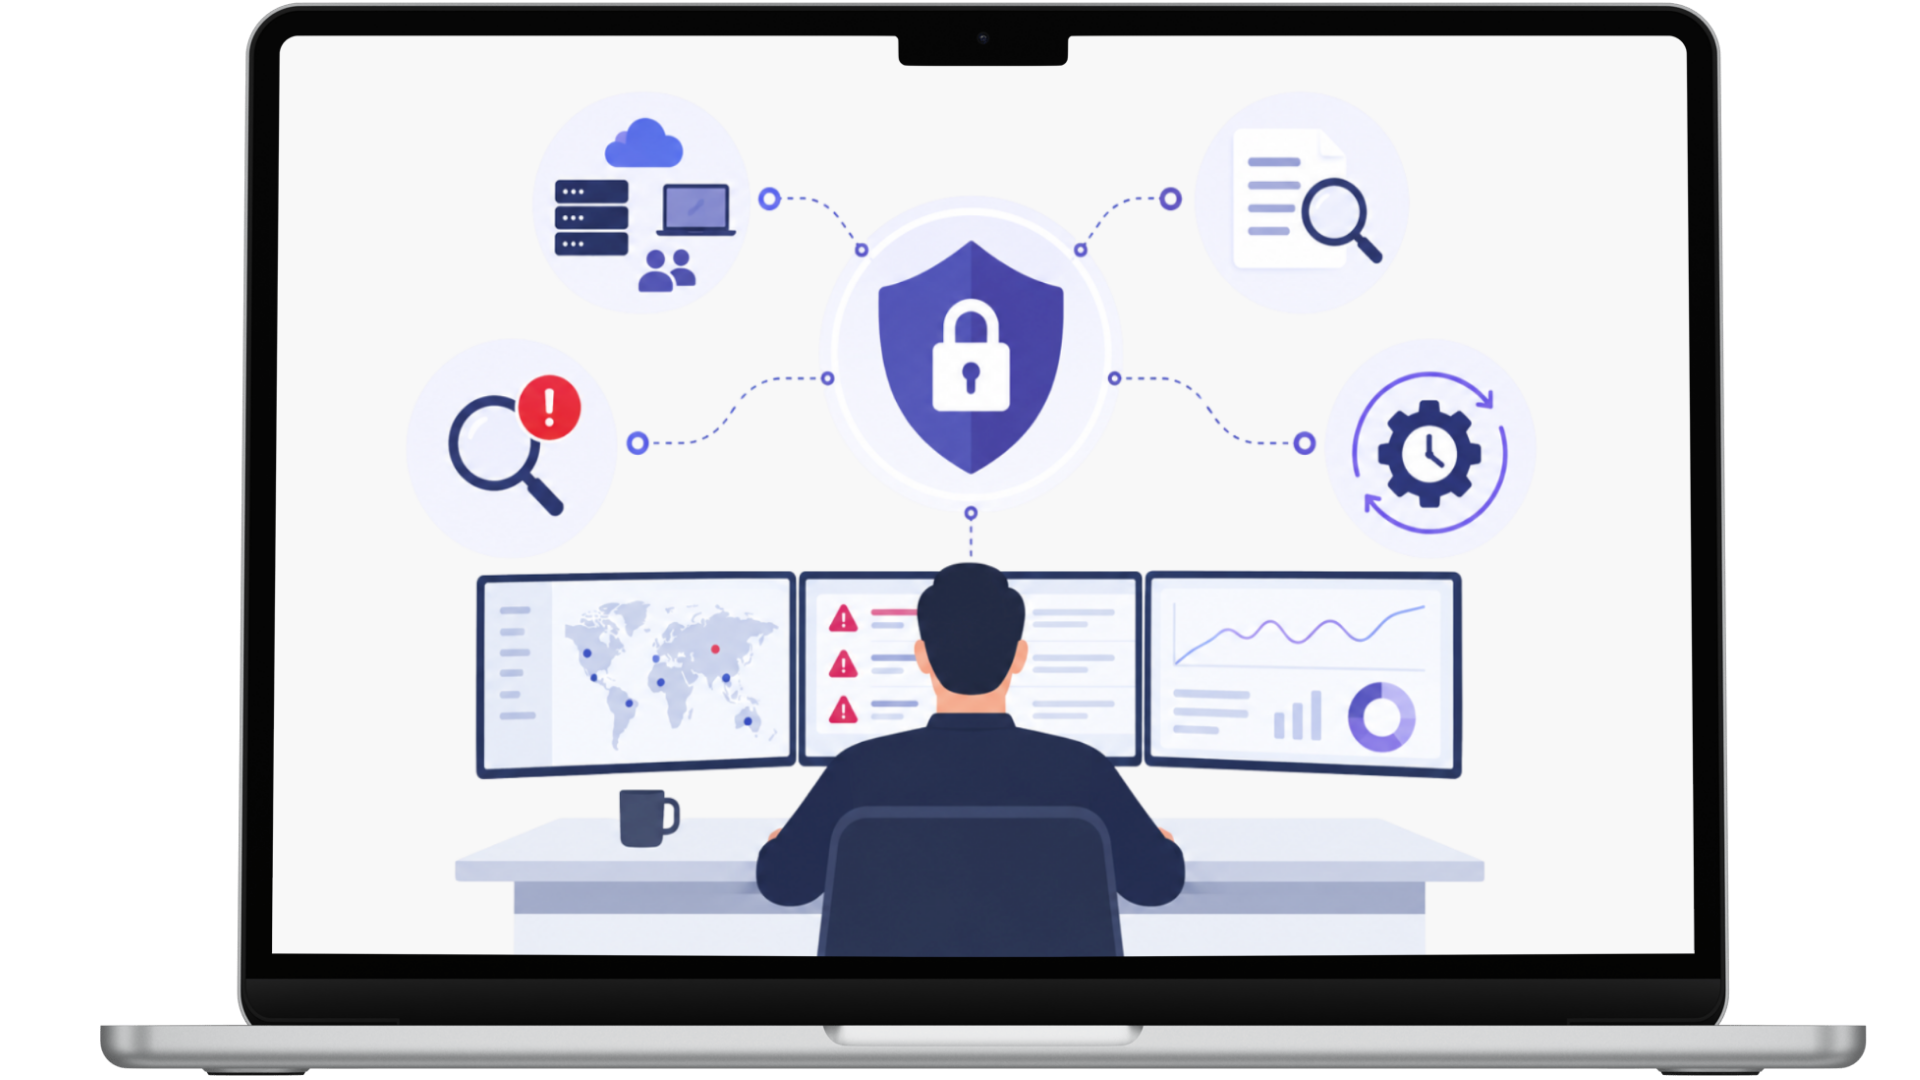
Detect
Use AI-assisted threat detection and behavioural analytics to identify abnormal behaviour, suspicious patterns and emerging threats.
Respond
Security events can be escalated and response activities coordinated when genuine incidents are identified.
Monitor
Maintain 24x7x365 visibility across users, endpoints, servers, cloud platforms, Microsoft 365 services and network infrastructure.
Detect
Use AI-assisted threat detection and behavioural analytics to identify abnormal behaviour, suspicious patterns and emerging threats.
Investigate
Experienced security analysts review significant alerts, validate potential threats and determine what requires action.
Respond
Security events can be escalated and response activities coordinated when genuine incidents are identified.
COMPLETE SECURITY VISIBILITY
Bring security activity across your environment into view
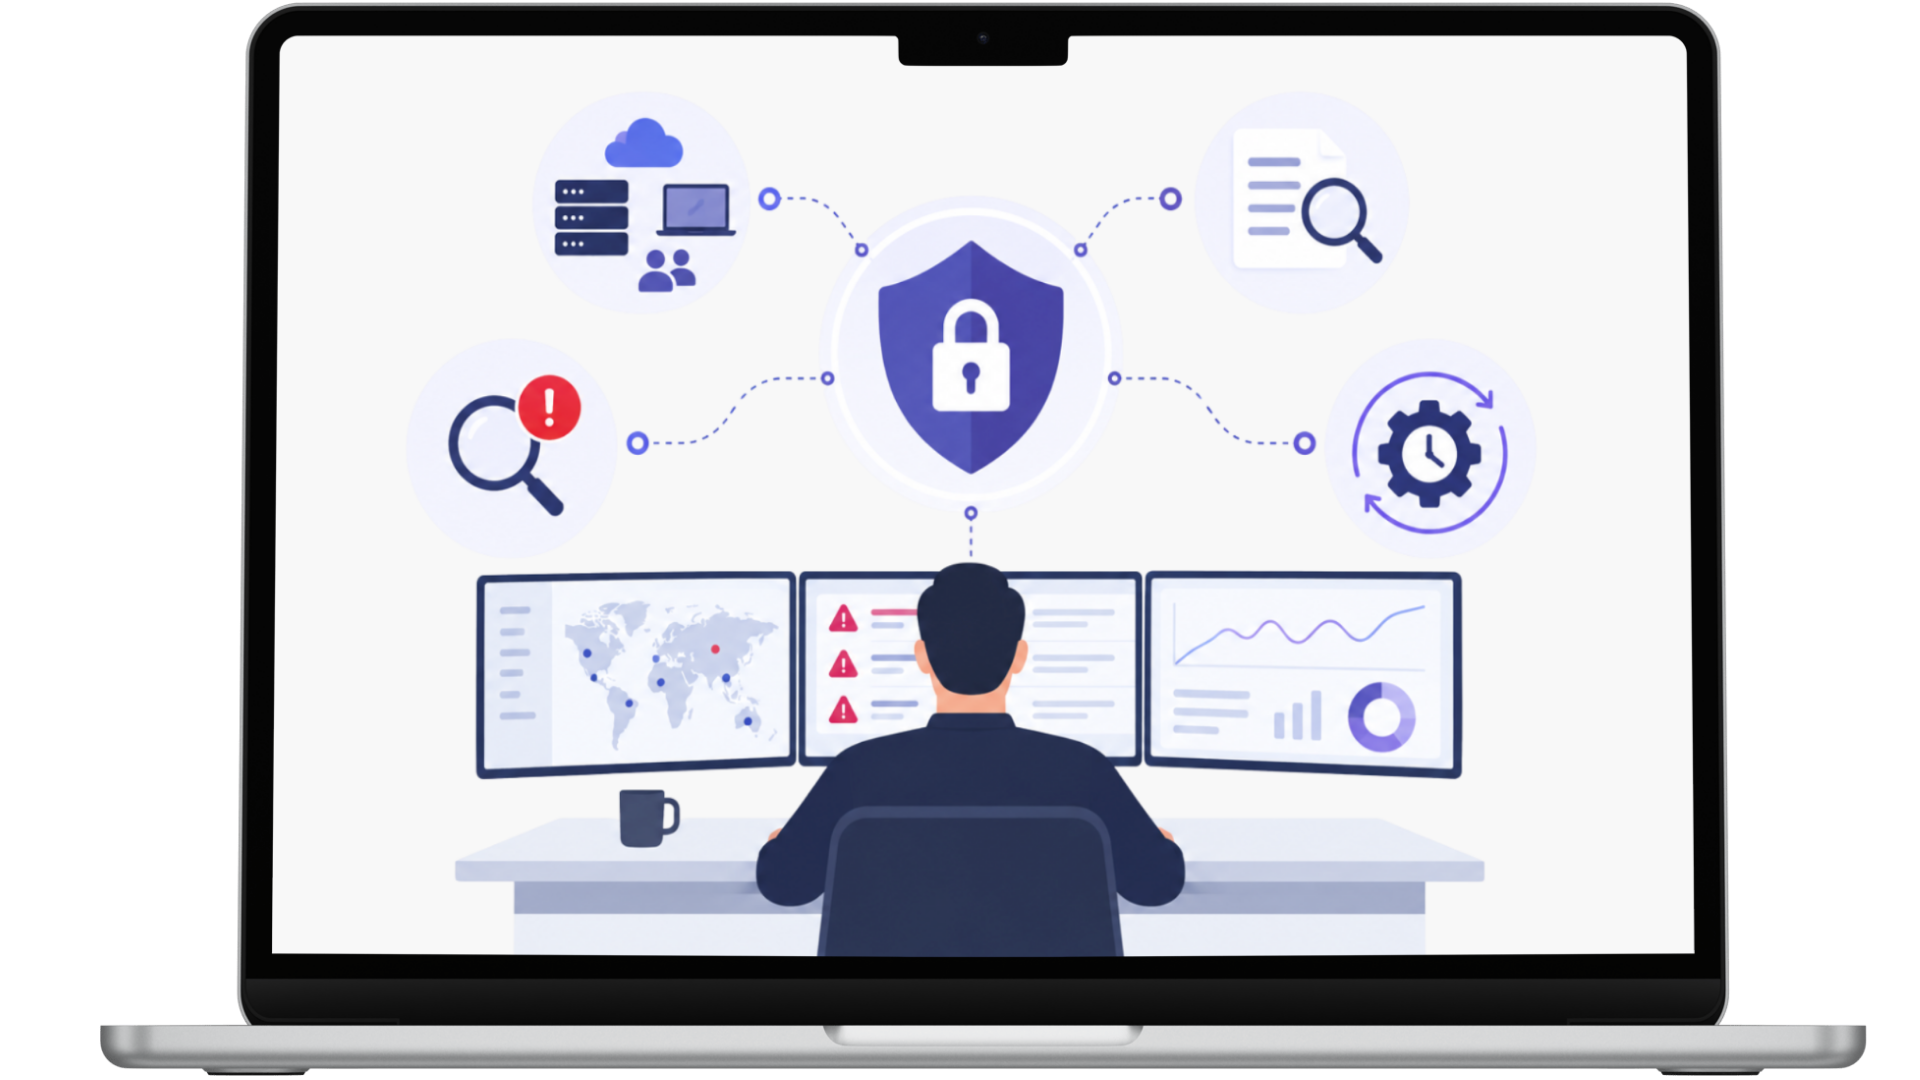
SOC & SIEM monitors and correlates security activity across multiple systems, giving HDUK's security team greater visibility into suspicious behaviour across your IT estate.
Users & identities
Monitor user activity to help identify suspicious behaviour and potential security events.
Endpoints & servers
Bring security activity from endpoints and servers into the wider monitoring environment.
Microsoft 365 & cloud
Monitor security activity across Microsoft 365 services and cloud platforms as part of the wider IT estate.
Network infrastructure
Extend monitoring across network infrastructure to provide broader visibility into security activity.
AI finds the signals. Security analysts determine what matters.
HDUK's SOC & SIEM platform uses artificial intelligence and machine learning to continuously analyse security activity, identifying abnormal behaviour, suspicious patterns and emerging threats in real time. Significant alerts are then reviewed and investigated by experienced security analysts.
Intelligent analysis
AI-assisted analysis helps uncover risks that traditional rule-based security tools can miss while helping reduce false positives and alert fatigue.
Human investigation
Experienced analysts investigate significant alerts, validate potential threats and determine when escalation or response is required.
Faster, more focused response
Combining intelligent technology with human expertise helps genuine security incidents to be identified and addressed quickly.
BUSINESS BENEFITS
What SOC & SIEM means for your organisation
MANAGED SOC & SIEM
Technology-led detection. Human-led investigation.
HDUK combines intelligent security technology with experienced analysts who investigate significant alerts, validate potential threats and support an appropriate response.
24/7 monitoring
Security activity across your IT environment is monitored around the clock through HDUK's Security Operations Centre.
AI-assisted detection
Artificial intelligence, machine learning and behavioural analytics help identify abnormal activity and emerging threats.
Human analyst validation
Experienced security analysts review and investigate significant alerts rather than relying solely on automated detection.
Threat hunting & intelligence
Threat intelligence and threat hunting provide an additional proactive layer for identifying suspicious and emerging security activity.
We gradually worked through the problems and migrated from what was becoming an old unusable cloud solution to a snappy easily managed one using Office 365, this has been a complete revelation to the way we work. I am now paying less money than I was this time last year too.
Trefor Wilkinson, The UK Career Academy Foundation
+
Years of experience providing IT Solutions
+
Professional firms supported
k+
Users taking benefit from our solutions
TRUSTED BY PROFESSIONAL FIRMS
Ready for greater visibility across your security environment?
Tell us how you're monitoring cyber security today and where you need greater visibility or support. Submit your details and our team will get in touch to discuss your current environment and SOC & SIEM requirements.